Mainline kernel devs applied the fix upstream on October 5, ten days before the CVE was published
Debian’s kernel team imports entire upstream stable point releases rather than backporting individual CVE patches into heavily patched kernel trees like some of the other distros. Once the fix shipped in the 6.12.113, 6.1.190 and 7.2.10 stable releases, it arrived in Debian unstable/sid as part of a routine version bump
Then a day after the cve was published and marked as 9.8 (16th) Debian also patched the frozen versions like Trixie and bookworm

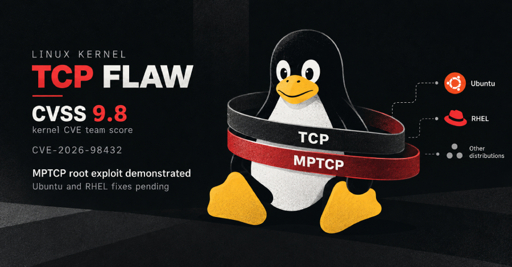
Debian was patched much earlier, how?
Mainline kernel devs applied the fix upstream on October 5, ten days before the CVE was published
Debian’s kernel team imports entire upstream stable point releases rather than backporting individual CVE patches into heavily patched kernel trees like some of the other distros. Once the fix shipped in the 6.12.113, 6.1.190 and 7.2.10 stable releases, it arrived in Debian unstable/sid as part of a routine version bump
Then a day after the cve was published and marked as 9.8 (16th) Debian also patched the frozen versions like Trixie and bookworm
sounds like another vote in the debian column
They fixed the bug shortly after it was known not only after it got a catastrophic score.